How to Use Copilot Managed Runtime
Build and deploy a Copilot Managed Runtime app with the CLI, then check identity, connectors, preview access and billing limits.

You can take an AI-generated internal app, keep editing it in a real Git repository, and move it from localhost to a Microsoft-hosted app without separately assembling hosting, sign-in, connector, deployment, and monitoring systems. Copilot Managed Runtime entered public preview on September 25, 2026, and the available developer path is the Copilot Managed Runtime SDK plus its ms command-line tool. The business win is not faster code generation. It is replacing a pile of platform work with one governed route into your Microsoft 365 tenant. The catch is that your tenant, connector policy, and runtime coverage decide whether that route opens.
What Copilot Managed Runtime actually is
Copilot Managed Runtime is a managed home for internal business apps. Your code remains editable, source control remains real Git, and Microsoft supplies the hosted runtime, Microsoft Entra sign-in, governed data connections, preview and deployment mechanics, and an admin inventory.
Think of it as a serviced office building for code. You still design what happens inside each room. The building supplies the badge desk, utilities, safety rules, maintenance log, and facilities team. That is different from an AI coding surface that only produces the room layout.
Microsoft describes the SDK as the developer layer for internal line-of-business apps. It includes Entra authentication without custom identity code and access to more than 1,500 connectors from JavaScript and TypeScript, though tenant policy determines which connectors and actions your app can actually use. The public-preview SDK overview and launch announcement are the useful boundaries here.
This guide follows the SDK and CLI that are available now. It does not treat Copilot Code or Autopilot as interchangeable names for that toolchain.
Where the app actually lives
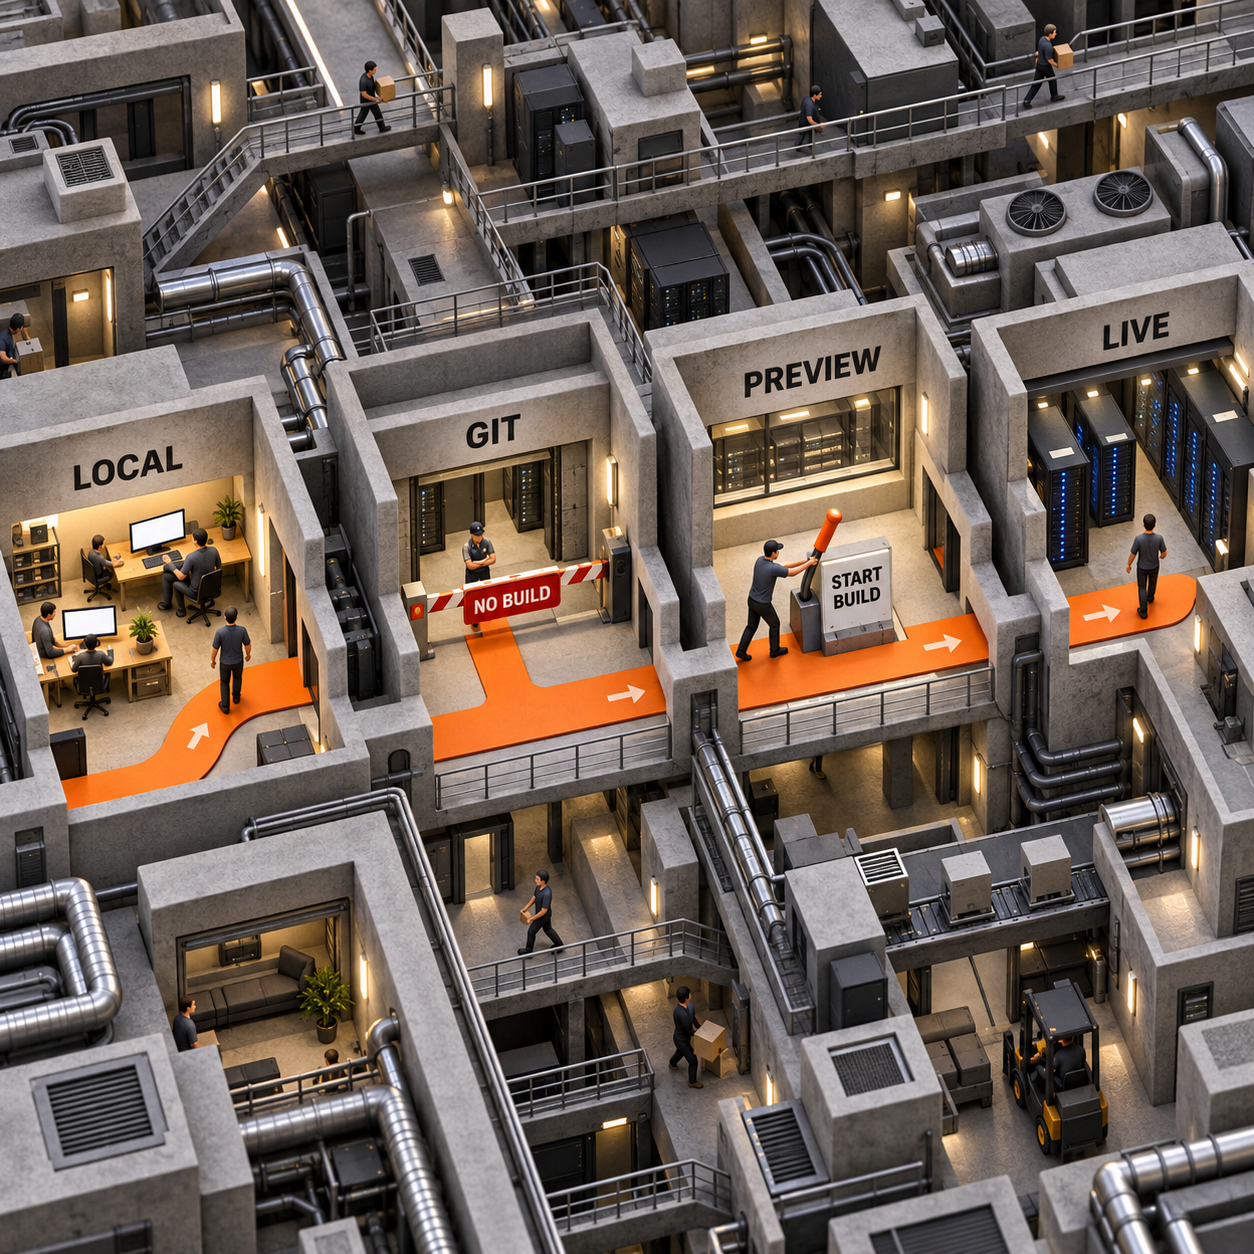
The answer changes as the app moves through its lifecycle:
That separation matters. Preview can move while live stays stable, and a failed preview build does not replace the last successful version.
Start with the gates, not the code
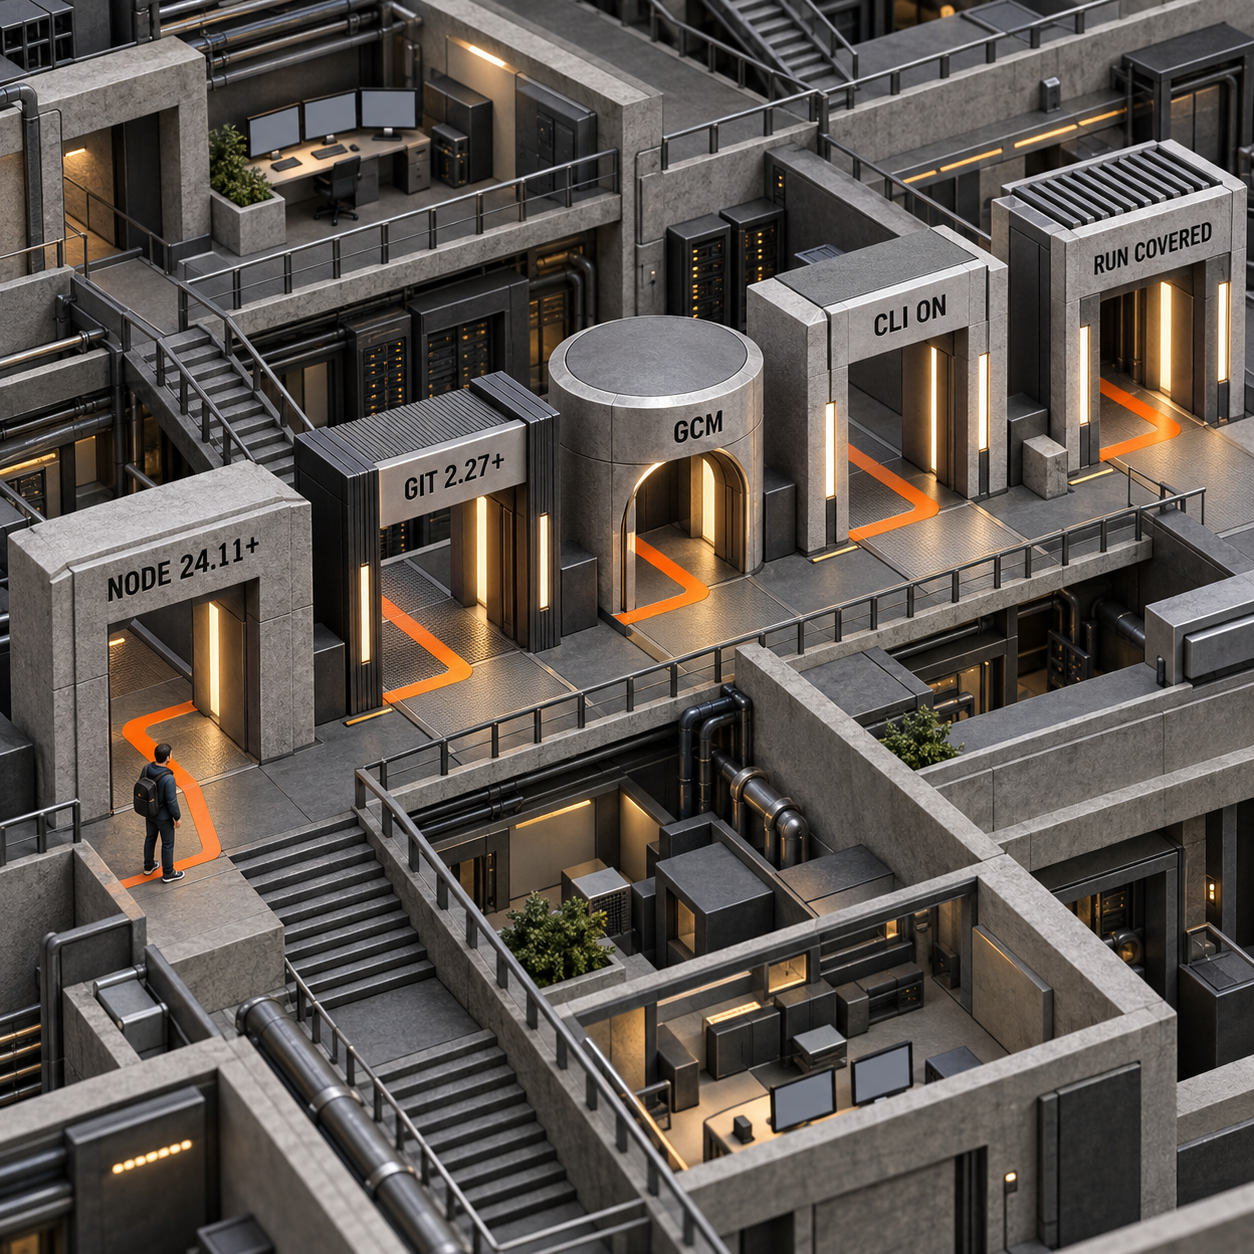
The fastest way to waste a day is to discover the tenant or license gate after the app is ready. Check these five items first.
The billing choices and admin policies deserve their own budget decision. Use the separate Copilot Managed Runtime pricing breakdown before you give a pilot group access. One operational detail belongs in this guide: local execution is not a free loophole. It needs the same runtime coverage as an end user.
What was verified for this guide
The package check was real. The tenant run was not.
That means there is no claimed time to first local page or hosted preview, no observed build failure, no inspected Entra identity, no executed connector call, no deployment, and no runtime bill in this article. The steps below are the documented Microsoft path, not a disguised lab result.
Take one small operations app through the CLI
Use a synthetic app called Ops Intake. Its first job is modest: display records from one tenant-approved source in a read-only queue. Starting with a read operation keeps the first policy review understandable. Add writes only after identity, source permissions, connector policy, and runtime coverage are proven.
For reproducibility, this sequence pins the CLI version verified on September 27, 2026. Record your own chosen version in the repository so a preview package update cannot silently change the pilot.
npm install -g @microsoft/managed-apps-cli@0.25.1
ms --version

ms auth login
ms app create ops-intake --display-name "Ops Intake"
cd ops-intake

npm install
ms app dev

ms connector list --search SharePoint
ms connector list-actions --connector <allowed-connector-id> --search list
ms app add data-source --connector <allowed-connector-id>

git add .
git commit -m "first ops intake flow"
git push

ms app play --mode preview
ms app build-status
ms app deploy
Here is what each transition means.
1. Sign in and create the governed shell
ms auth login opens Microsoft Entra sign-in. On a headless machine, the CLI also offers --device-code. ms app create creates the app record, scaffolds the project, and uses a platform-managed Git repository by default. The first create or init also provisions the maker's identity-scoped developer environment if routing permits it.
Do not choose a repository mode casually. Platform-managed Git is the shortest start. An external repository can be GitHub.com or GitHub Enterprise Cloud. GitHub Enterprise Server, Azure DevOps, and other providers are not supported for this path. The repository mode is fixed for the life of the app, so changing it later means creating another app.
2. Run locally and record the first useful time
Install the scaffolded dependencies once, then run ms app dev. The command reads ms.config.json, starts the project's development process, and prints a Local Play URL. Open it in the same browser profile used for the tenant.
Start a timer immediately before ms app dev, then stop it when the first usable page renders. Record browser permission interruptions separately. Chrome and Microsoft Edge can block a public origin from reaching localhost until local-network access is granted, which is a browser gate rather than an application build failure.
3. Prove one governed read
ms connector list shows connector IDs, authentication type, tabular support, and both Data Loss Prevention and Advanced Connector Policy status. Use that output as the source of truth for the environment. A connector that exists in Microsoft's catalog is not automatically allowed in your tenant.
For Ops Intake, select an allowed SharePoint connection, dataset, and list, then choose a read or list operation. The interactive ms app add data-source flow generates typed TypeScript models and services under generated/. Call the generated read method from the app rather than inventing a raw Graph token flow.
Validate three things in the browser:
- The signed-in user is the expected Entra identity.
- The user sees only records already permitted by the source system.
- The app fails safely when the same user loses source access.
Sharing the app later does not grant access to the underlying data. Every recipient still needs the right source permissions and connection. That is a feature, not a deployment nuisance.
4. Commit and push real source
Use ordinary Git commands. The runtime CLI does not replace source control. Your commit should include the working application change and the generated connector bindings that belong in the project.
The important trap is simple: git push does not build the app. It only updates the remote source of truth.
5. Open hosted preview and inspect the build
ms app play --mode preview opens the stable preview endpoint. If the latest pushed commit has no build, opening preview queues one. Record the time from opening preview until the new version is ready.
If the build fails, run ms app build-status, optionally with --commit <sha>, and save the complete reason next to the commit. Preview continues serving the previous successful build when a newer one is still building or has failed. The preview URL is for developers with write access to the repository, not arbitrary reviewers.
You can run ms app build when you want to start a build before opening preview. Most teams should first learn the default behavior: push source, then open preview.
6. Deploy only the version you inspected
ms app deploy promotes a successful build to the live app. Live is a fixed snapshot. It does not follow every push or preview build.
For a deliberate release, record the commit SHA, check build status, open its preview, then deploy that SHA with ms app deploy --commit <sha>. The same option gives you a clean rollback to an earlier successful build without rewriting Git history.
The business math changes at the platform layer
The runtime does not make application work free. It changes which parts your team must buy or build separately.
The comparable software budget is not trivial. Retool's official pricing page lists its Team tier at $10 per builder and $5 per internal user per month, and its Business tier at $50 per builder and $15 per internal user per month. Copilot Managed Runtime does not automatically beat that number. It can remove separate platform work for a Microsoft 365 organization, while its runtime licenses, credits, connector work, and admin time remain real costs.
Use this pilot equation before calling it cheaper:
Pilot cost = developer time + admin setup + runtime coverage + connector and data work.
The line most likely to shrink is platform assembly. The line most likely to surprise you is runtime coverage across every user who opens the app.
Seven internal apps that fit this runtime
The best candidates are internal workflows where identity, governed Microsoft 365 data, and controlled release matter more than a public storefront.
Each use case should begin read-only. A write action, external endpoint, third-party connector, or broadly shared app changes the review. The default policy includes 18 Microsoft first-party connectors, not the whole catalog, and it blocks some open-ended HTTP, arbitrary-code, arbitrary-query, and arbitrary-platform actions even inside approved connectors.
Three products worth building around the runtime
The strongest product is a Microsoft 365 onboarding command center. It combines the largest measured demand with a workflow that naturally spans identity, documents, tasks, mail, and team handoffs.
1. A Microsoft 365 onboarding command center
Build one internal app where HR and IT can see an approved new-hire record, outstanding tasks, document links, and ownership. HR operations and IT service teams would pay for fewer missed handoffs and a simpler audit trail.
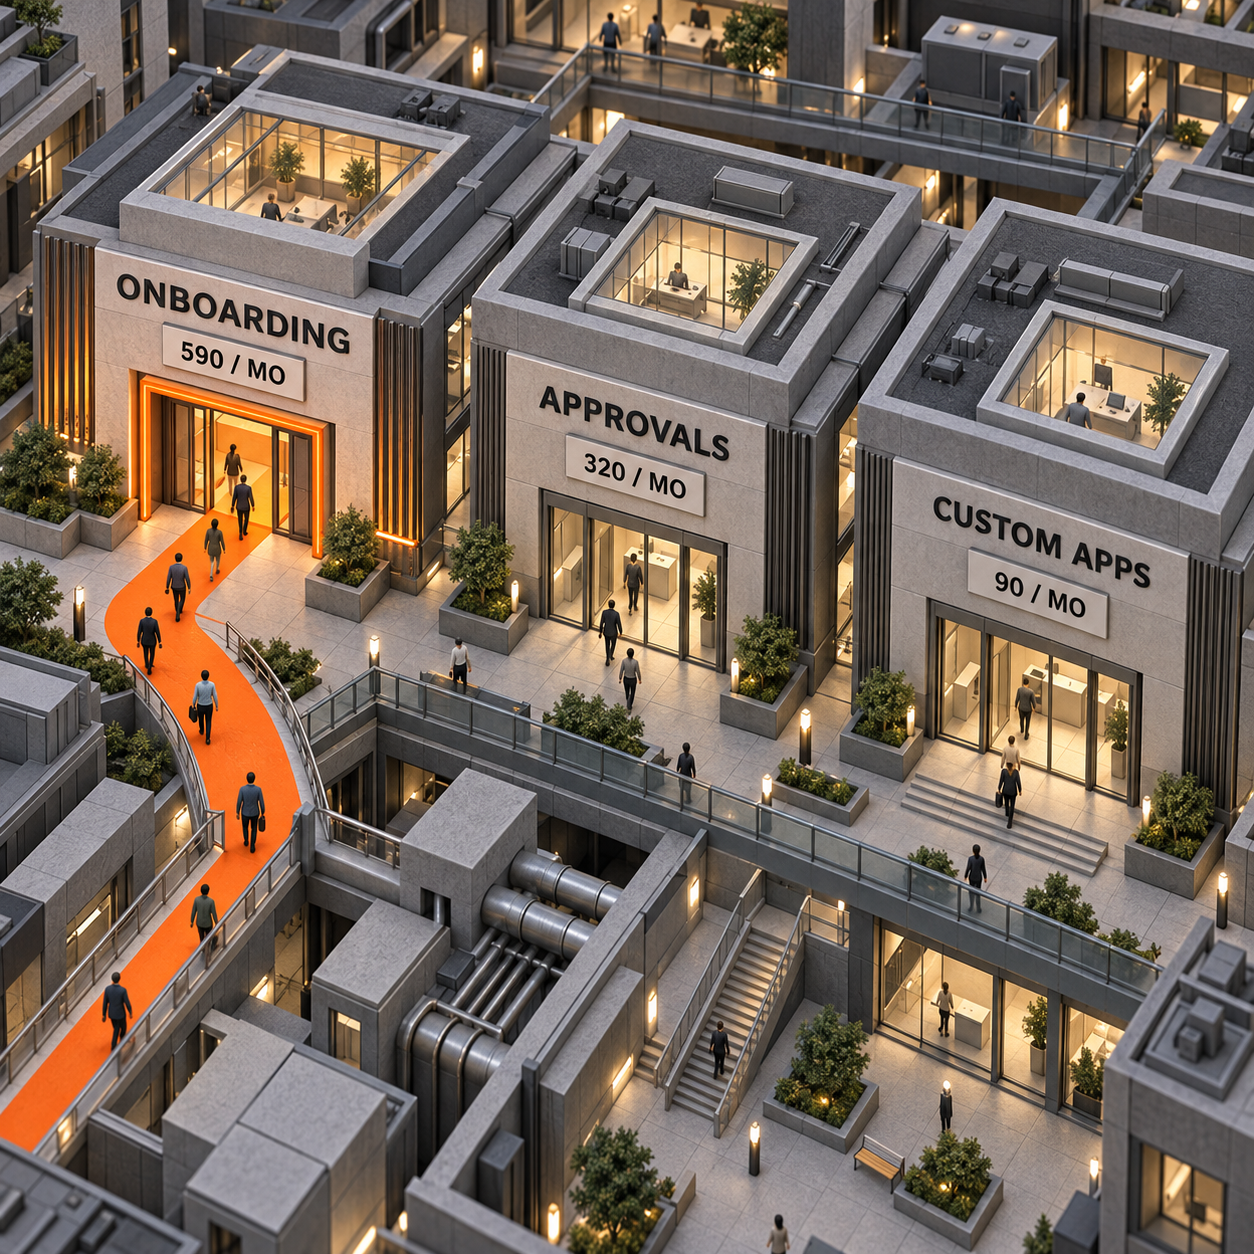
The demand is visible: “employee onboarding software” receives about 590 US searches a month, with commercial intent and a $156.35 cost per click. The narrower “best employee onboarding software” receives 90 searches a month and showed 180% yearly trend growth in the suggestion data.
The smallest sellable version serves one department, reads one approved employee list, displays a task checklist, and links each task to its owner. Add connector actions only after the read path passes policy and permission tests.
The catch is serious. HR data is sensitive, source permissions are easy to misunderstand, and established onboarding vendors already cover broader HR workflows. The product wins only when Microsoft 365 governance and tenant-native operation matter more than a long generic feature list.
2. A governed approval cockpit
Build a reusable approval surface for finance, procurement, or operations teams that have a clear decision state but scattered supporting context. A buyer pays for faster review and a controlled release process, not another form builder.
“Approval workflow software” receives about 320 US searches a month, with commercial intent, a $114.86 cost per click, and 53% yearly trend growth in the suggestion data. That combination signals an active buying problem with room for a focused Microsoft 365 implementation.
The MVP is one request type, one approved source, a read-only review screen, decision history, and a single policy-approved action. Keep the decision model deterministic. Do not hide approval rules inside generated prose.
The catch is connector policy. A connector can be allowed while a particular action remains blocked, and classic data policies can combine with Advanced Connector Policies so the most restrictive result wins.
3. A managed-app migration assessment
Sell a productized assessment that takes one AI-generated or custom internal web app and determines whether it can move into Copilot Managed Runtime. The buyer is a Microsoft 365 organization with a useful prototype and no appetite for another standalone hosting and governance stack.
“Custom business app development” receives about 90 US searches a month, with commercial intent and an $84.03 cost per click. The volume is smaller, but the query sits close to a services purchase.
The MVP inventories the app's repository, runtime assumptions, external endpoints, identity code, data sources, and required actions. It then produces a pass, change, or stop decision and ports one read-only slice into a test environment.
The catch is platform concentration. The result is useful only for eligible Microsoft 365 tenants, public preview behavior can change, and unsupported source providers or blocked external resources can make a seemingly simple migration a rebuild.
What Copilot Managed Runtime does not solve
This is a promising route for governed internal apps, not a universal application platform.
- It is a public-preview feature with prerelease documentation. Treat command behavior and policy surfaces as changeable.
- It does not make the CLI creation path available automatically. That path is off by default, even when the tenant is eligible for the runtime.
- It does not turn all 1,500-plus connectors into allowed data sources. Tenant policy, connector action policy, classic data policies, and source permissions still decide access.
- It does not make a public customer-facing product from an internal line-of-business app. Preview is limited to developers with repository write access, while live access is shared deliberately inside the governed model.
- It does not support every repository provider. External source is limited to GitHub.com and GitHub Enterprise Cloud, and the repository mode cannot be changed in place.
- It does not remove runtime licensing. Local execution and user execution require Power Apps Premium or funded Managed Application Copilot Credits.
- It does not give administrators a perfect forensic record. The admin view covers inventory, usage, health, connectors, data sources, and dependencies, but Microsoft says it is not a complete view of exact destinations, dynamic endpoints, actions executed, or each user's effective source permissions.
- It does not prove this desk's deployment. Missing Git Credential Manager, a missing Linux secret-store library, and the absence of an eligible tenant stopped the run before sign-in.
The honest decision is narrow: use it when your app is internal, your organization already lives in Microsoft 365, and the avoided identity and governance work is worth accepting a preview platform and its tenant controls. Use a different host when you need a public SaaS product, another source provider, infrastructure control, or a release model your administrators cannot permit.
Frequently asked questions
How do I run my Copilot agent?
Copilot Managed Runtime's CLI path runs internal apps, not a generic agent process. Run the app locally with ms app dev, open a hosted developer build with ms app play --mode preview, and promote a successful build with ms app deploy. If you mean a conversational Copilot agent, use that agent product's runtime instructions instead.
How do you use Copilot for beginners?
For this capability, start with an administrator-enabled test user, one tiny internal app, and one allowed read-only connector. Verify Node, Git, Git Credential Manager, CLI version, environment routing, and runtime coverage before ms auth login and ms app create.
Is there a way to track Copilot usage?
For Copilot Managed Runtime apps, administrators can inspect inventory, usage analytics, health, policy, connectors, and dependencies in Microsoft 365 admin center. That is app-level operational visibility, not a claim about every Copilot product.
Can an employer see Copilot chats?
The Managed Runtime documentation used here does not establish employer access to Copilot chat transcripts. It documents app inventory, usage, health, policy, connectors, data sources, and dependencies. Do not turn those app controls into a broader claim about chat visibility.
The Monday move
Ask a Power Platform Administrator to enable CLI creation for one test group, confirm the group's environment-routing rule, and cover two test users for runtime. Pick one non-sensitive SharePoint list and one read-only operation. Then have a developer record four facts in the pilot log: CLI version, time to first local page, time to hosted preview, and the commit SHA deployed. Stop the pilot if Entra identity, source permissions, or connector policy behaves differently from the written expectation.
- Last Updated
- Sep 27, 2026
- Category
- Build
Prefer this site in Google


Mark omidsaffari.com as preferred and Google lifts it in Top Stories, AI Overviews and AI Mode for you.
How to Use GPT-6 Prompt Caching
Set up GPT-6 prompt caching, diagnose misses, and measure cache reads, writes and cost in a repeatable agent workflow.Sep 27, 2026Build
Copilot Managed Runtime Pricing
Separate Copilot Managed Runtime build costs, runtime credits and Power Apps Premium coverage before budgeting an internal AI app.Sep 26, 2026Build
n8n Agents vs Workflows
Choose between n8n Agents and workflows for support and operations, with execution costs, approvals and the limits of the new preview.Sep 26, 2026Build
Is Jev Router Free
Jev Router's catalog says $0. Check what that covers, the cost of routed model calls and the usage records before budgeting an agent.Sep 26, 2026Build
How to Publish Claude Plugins
Publish a Claude plugin through the new directory portal. Check paid-plan access, choose a bundle or MCP connector, and prepare for review.Sep 26, 2026Build
Is Cloudflare MCP Portals Free
Check Cloudflare MCP Portals' free-plan limits, paid seats and separate model or server costs before connecting your team's agents.Sep 26, 2026Build
How to Use Agentic CUDA Optimizer
Set up the CUDA optimizer, run a bounded kernel experiment, and check correctness, GPU time and model costs before trusting a speedup.Sep 25, 2026Build