Cloudflare Can Stop AI Spend Landing on the Wrong Bill
Cloudflare AI Gateway can require your provider credentials. Learn when missing keys stop a request and which charges stay separate.



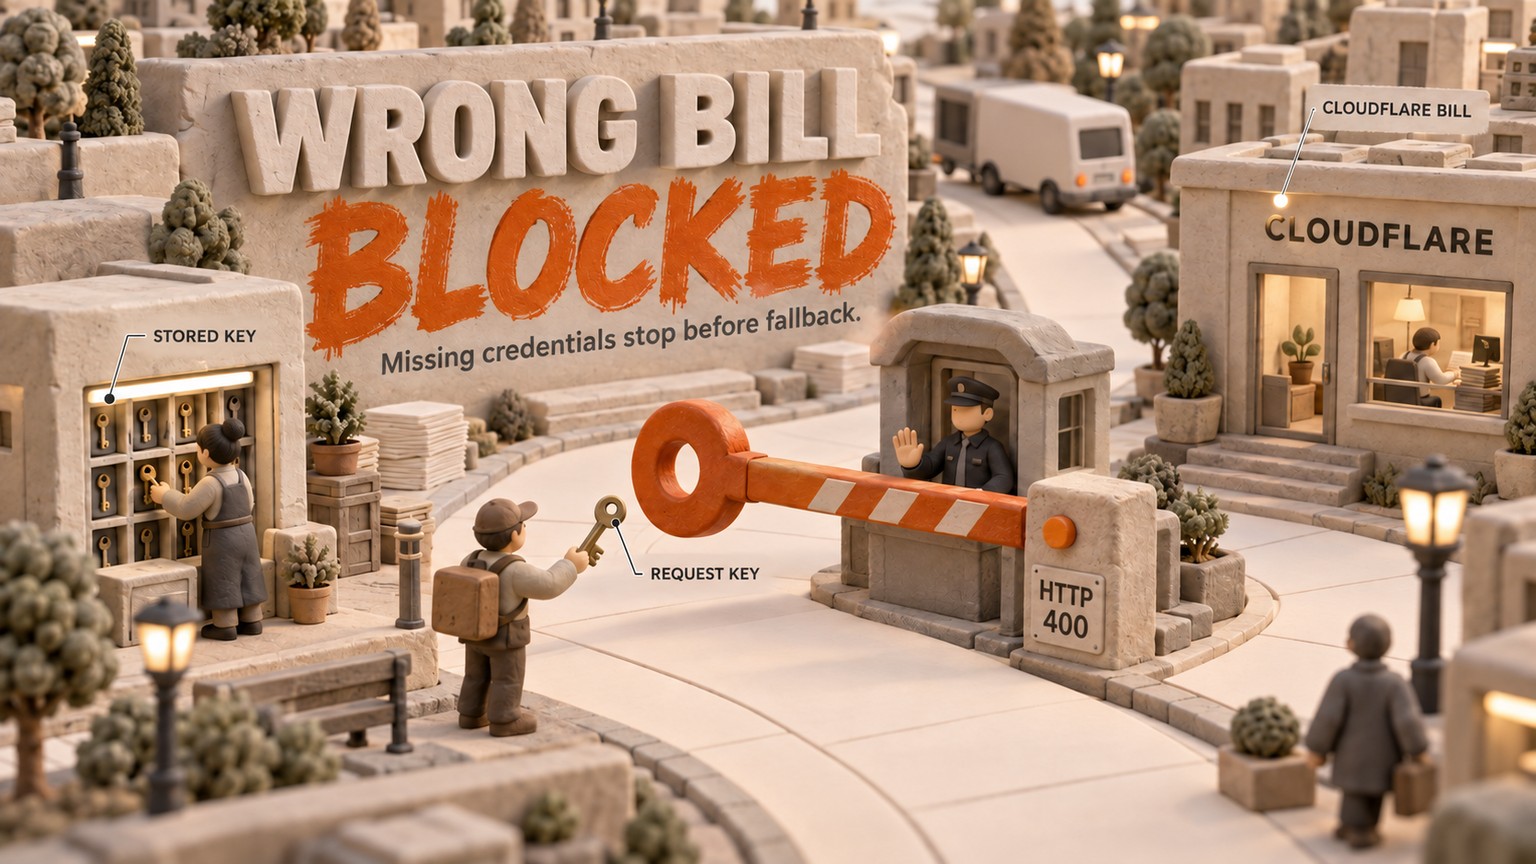
Cloudflare can now make a missing client model key fail before the request lands on your Cloudflare AI bill. On September 14, 2026, AI Gateway added a provider-credential requirement that turns a third-party request with no applicable key into HTTP 400 instead of Unified Billing usage.
The change is about who pays
AI Gateway can send one model request through several credential paths. A credential is the key that tells the upstream model provider which account should pay.
Before this change, the order was simple. Cloudflare first looked for a provider key on the request. If none was there, it looked for a Bring Your Own Key, or BYOK, stored on the gateway under the default alias. If neither existed, it could use Cloudflare-managed credentials through Unified Billing and deduct the usage from your Cloudflare credit balance.
That final fallback is useful when you want Cloudflare to be the payer. It is a budget leak when the request belongs to a client who was meant to supply their own OpenAI, Anthropic, Google, or other provider key.
Cloudflare now lets you remove that third step for third-party provider traffic. Turn on Require provider credentials for the gateway, represented as byok_only: true in the API, and a request with no applicable customer credential stops with HTTP 400. You can apply the same restriction to one request with cf-aig-no-wholesale: true. Cloudflare documents the full credential order and both controls here.
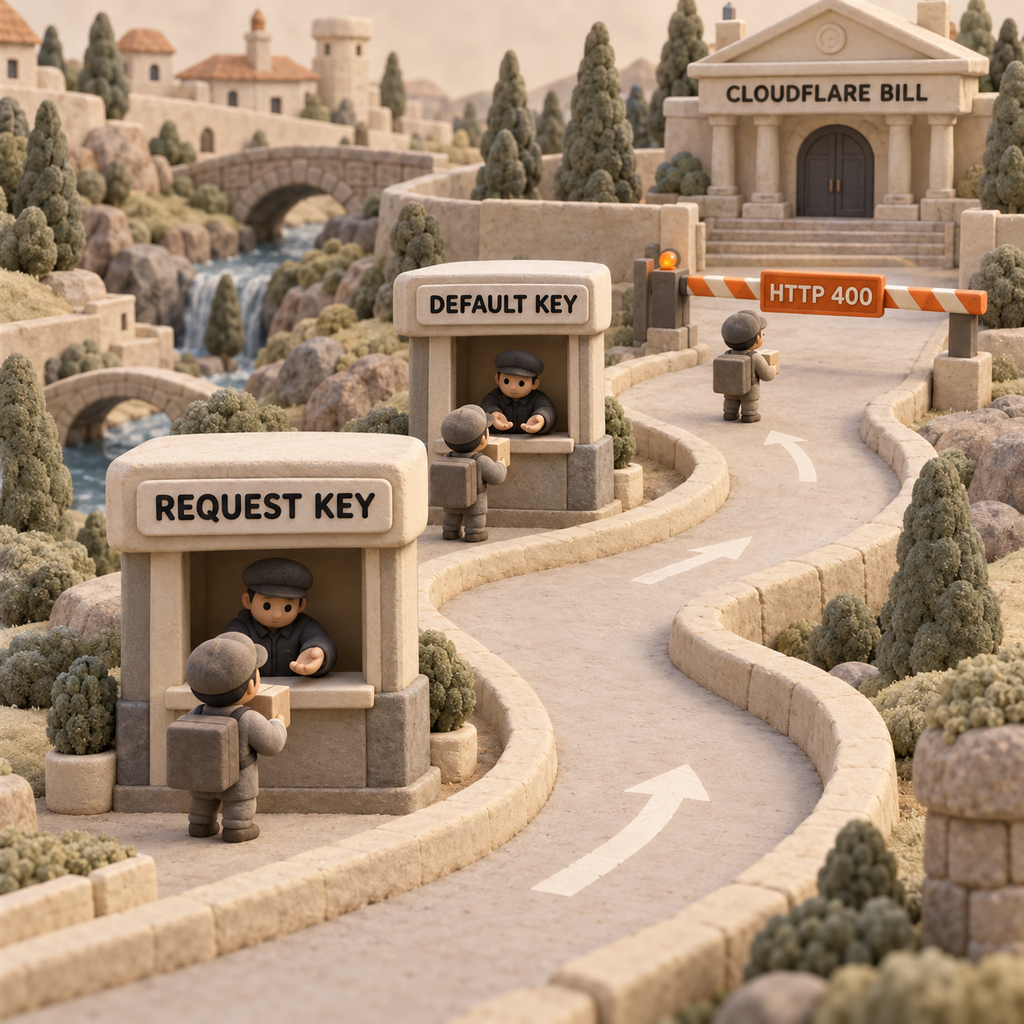
The easiest way to understand it is as three possible payers in a queue:
- Request credential: The client sends its provider key with that call. AI Gateway forwards it unchanged, so the provider bills the account behind that key.
- Stored gateway credential: No provider key arrives with the call, so AI Gateway uses a provider key saved in Cloudflare Secrets Store. On Unified Billing endpoints, the applicable stored key must use the
defaultalias. - Cloudflare Unified Billing: No applicable client or stored key exists, so Cloudflare can use its managed credential and deduct credits from the Cloudflare account.
The new rule says the queue ends after step two. That is the whole business consequence: missing credentials become visible downtime instead of invisible cost transfer.
The cost math moved from reconciliation to rejection
Unified Billing adds a 5% fee when you buy credits. Cloudflare's own example is clean: $100 of credits produces a $105 charge, while the provider's inference price itself passes through without markup.
Now put that into a client workflow. If a client job was meant to use the client's provider account but its key went missing, $100 of model usage could consume the operator's Cloudflare credits instead. Funding those credits costs $105. The client provider account records none of that fallback usage, while the operator owns the whole $105 cash charge and then has to prove which client caused it.
The 5% fee is not the main problem. The main problem is that the entire $100 workload moved to the wrong budget. The extra $5 simply makes the mistake more expensive.
Requiring provider credentials changes the failure from a finance investigation into an application error. You lose the automatic rescue, but you gain a hard boundary around the payer. For a broader comparison of gateway fees and direct-provider billing, see the AI gateway cost breakdown.
Who should use it
An agency running client automations
An agency may operate one Cloudflare account while each client brings its own model-provider agreement. Enable the gateway rule on client-funded routes. If onboarding misses a key or a rotation removes it, the job stops instead of using the agency's prepaid balance.
The payoff is clean charge ownership. The client either supplies a working credential or receives a configuration failure. The agency no longer needs to reverse-engineer a shared credit bill after the work has already run.
A SaaS team accepting customer-supplied keys
A SaaS product with customer-supplied provider keys can treat HTTP 400 as a setup state. The product can tell the customer that its provider credential is missing, then keep the request out of the platform's own Cloudflare credit pool.
This is especially useful when a successful response would hide the mistake. Without the restriction, the feature keeps working and the wrong company pays. With it, the product fails early enough to repair the account configuration.
A platform engineer changing one route first
The request header is the smaller rollout surface. Add cf-aig-no-wholesale: true to one third-party request path, test the missing-key behavior, and wire the error into monitoring before making the gateway-wide change.
The precedence is deliberately one-way. A request header can make a permissive gateway stricter. A request cannot set the header to false and weaken a gateway where Require provider credentials is already on. Cloudflare describes these restrictions as additive.
A FinOps owner separating payer control from budget control
Use this setting to decide which account may pay. Use AI Gateway spend limits to decide how much may be spent. They are different controls and should have different tests.
Spend limits can cover both BYOK and Unified Billing requests when Cloudflare knows the model price. They can be scoped by model, provider, or metadata. But the cost is a best-effort estimate, and Cloudflare tells you to use the provider dashboard for exact billing. Treat the provider-credential rule as the payer boundary and verify the spend ceiling separately.
Set it up without creating a mystery outage
Map each route to its intended payer
Separate third-party provider traffic from Workers AI. For every third-party route, write down whether the provider key should arrive on the request or come from the gateway's stored
defaultkey. Do not enable a fail-closed rule until that ownership is explicit.Choose the smallest enforcement scope
For one path, send
cf-aig-no-wholesale: true. For the whole gateway, open AI > AI Gateway, select the gateway, open Settings, turn on Require provider credentials, and confirm. An API-managed gateway usesbyok_only: truein its update request.Prove both valid credential paths
Send one staging request with the provider key attached. Then send one that relies on the stored key under
default. Confirm the intended provider account records the usage in each case. If your Unified Billing endpoint relies on a key calledproduction, fix the alias before continuing.Remove the key on purpose
In staging, send the same third-party request without a provider key and without an applicable stored
defaultkey. The expected result is HTTP400, not a successful model response. Confirm that your retry policy does not keep repeating this configuration error.Assign the error to a person and queue
Make the integration or platform owner responsible for this HTTP
400, because that owner controls request headers, stored secrets, and key rotation. Customer support may explain the failure, and finance may audit it, but neither team should own the fix.
The honest trade-offs
This setting exchanges silent fallback for visible failure. If Unified Billing was your deliberate availability path, turning it on removes that rescue for third-party provider requests. An expired or invalid request key is also forwarded to the provider rather than replaced by another billing path, so the upstream provider can still reject it.
Workers AI is the important exception. Workers AI requests do not use third-party provider credentials, remain allowed, and keep the gateway's separate Workers AI billing mode. Enabling byok_only is not a global “nothing can charge Cloudflare” switch.
Spend limits do not close every gap either. Their accounting is eventually consistent, which means concurrent requests can briefly take spend past a limit. They also estimate cost from tokens and known model prices. Use them, but reconcile exact charges against the provider and Cloudflare billing surfaces.
Your Monday move
Pick one client-funded third-party route. Add the request-level restriction first, then run the missing-credential test in staging. The pass condition is an owned HTTP 400 with no successful fallback. Put that error in the integration or platform team's queue, name the person who repairs the key, and only then consider enabling the rule across the gateway.
If your team intentionally uses Cloudflare Unified Billing for all third-party traffic, leave the rule off. If you use only Workers AI, this setting does not change that bill. If client or departmental provider accounts are supposed to pay, act this week and test the failure before the next key rotation tests it for you.
For more operator-ready explanations of changes like this, join the newsletter.
- Last Updated
- Sep 17, 2026
- Category
- Explained
Prefer this site in Google


Mark omidsaffari.com as preferred and Google lifts it in Top Stories, AI Overviews and AI Mode for you.
Cloudflare Lets Python Apps Reuse Existing Databases
Python Workers can connect through Hyperdrive. Check what that changes for an existing database, app architecture and hosting bill.Sep 16, 2026Explained
Gemini 3.8 Live Keeps Callers Talking During Lookups
Gemini 3.8 Live runs tools during voice calls. See what changes for booking flows, customer updates and the cost of a completed task.Sep 16, 2026Explained
Cloudflare Limits What a Client's Deploy Agent Can Change
Cloudflare adds access controls for individual Workers. See how to separate debugging, code review and deployment rights across client projects.Sep 15, 2026Explained
Claude Code Stops One Install From Widening the Whole Job
Claude Code can approve network hosts for one command at a time. See what that changes for dependency installs and unattended build jobs.Sep 15, 2026Explained
Vercel AI SDK Can Move Agent Spend to Existing Plans
Vercel AI SDK can use supported agent subscriptions. Check which credentials win, which allowance pays, and what sandbox costs remain.Sep 15, 2026Explained
Cloudflare Browser Run Keeps Client Jobs on Approved Hosts
Limit client browser jobs to approved hosts, budget for required CDNs, and let reviewers watch through read-only Live View.Sep 14, 2026Explained
GPT-Live-1 Changes the Budget for AI Phone Calls
Understand GPT-Live-1 phone-agent costs: the voice layer, backend reasoning, telephony, and the interruption handling worth testing.Sep 14, 2026Explained