Is Cloudflare MCP Portals Free
Check Cloudflare MCP Portals' free-plan limits, paid seats and separate model or server costs before connecting your team's agents.


Yes. Cloudflare MCP Portals is available on Cloudflare One's $0 Free plan for up to 50 active users. A 60-active-user team on Pay-as-you-go should budget $420 per month for seats, before the model, upstream SaaS subscriptions, a hosted MCP server, storage, or enterprise security features.
Is Cloudflare MCP Portals Free for Your Team?
Cloudflare MCP Server Portals is free when your organization stays within the 50-user limit of Cloudflare One Free and the Free plan's security and logging boundaries are enough. The portal itself does not have a separate per-tool-call price on Cloudflare's current plan table.
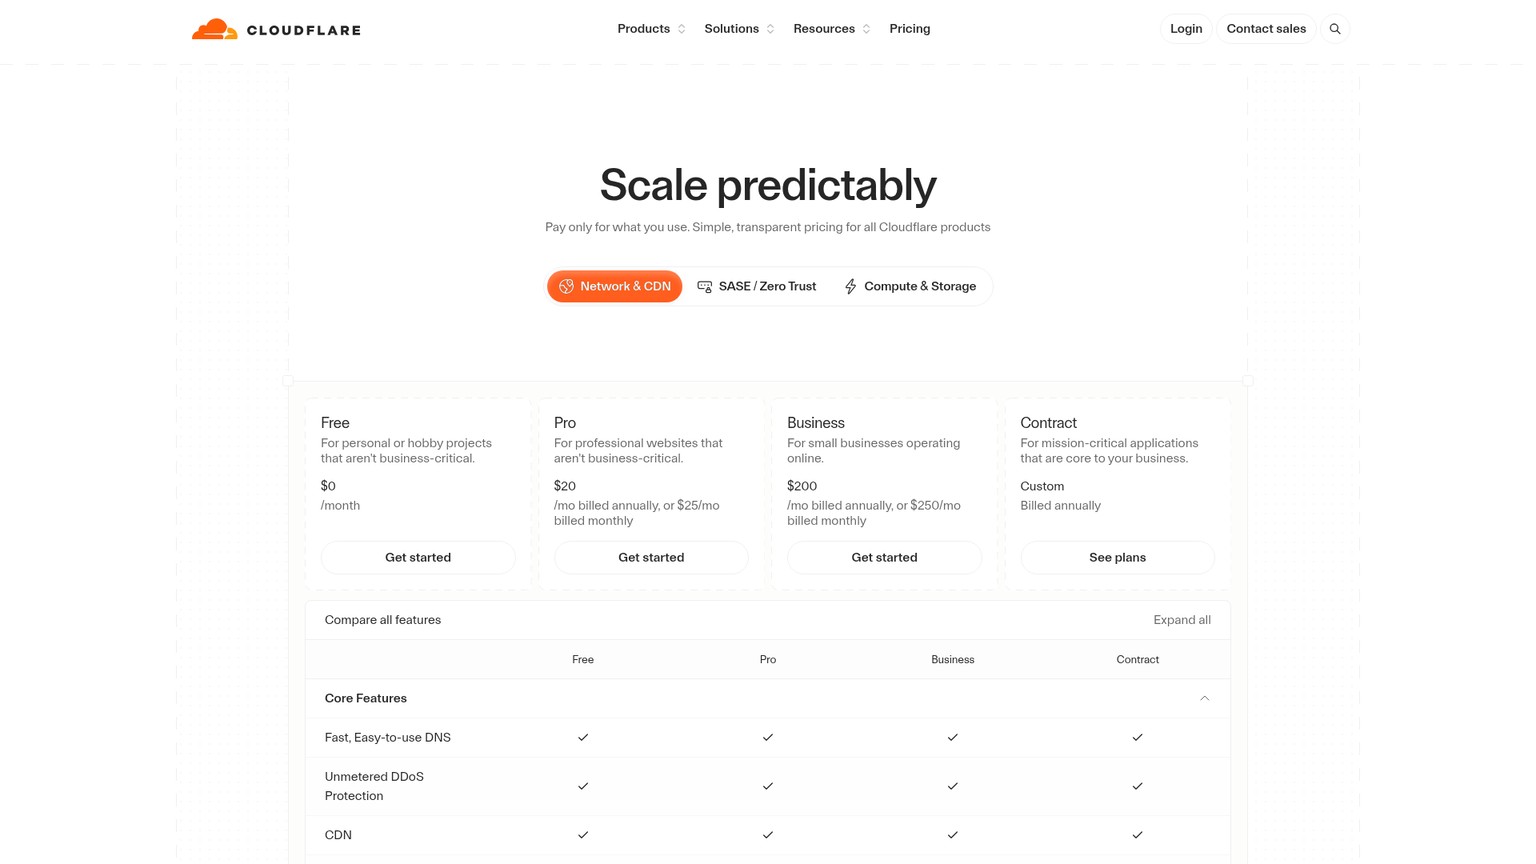
Cloudflare's live Zero Trust plan table lists these current boundaries:
That makes Free a credible small-team control plane, not a free agent stack. It can give approved users one endpoint for several MCP servers and record their activity. It does not include the model your agent runs, the subscription behind an upstream SaaS tool, or the compute that hosts a server you operate.
Pricing, limits, and entitlements in this guide were verified against Cloudflare's live public pages on September 26, 2026. No authenticated Cloudflare account was available for this review, so no dashboard bill or tool-call result is presented as an observed test.
What Actually Changed on September 24, 2026
The change was availability and production readiness, not a new standalone portal charge. On September 24, 2026, Cloudflare made MCP server portals generally available to all Cloudflare customers. The earlier beta had already been available across plans and advertised up to 50 free seats.
A portal is a governed front door for Model Context Protocol servers. An AI client connects to one portal endpoint, Cloudflare Access checks the person or service identity, and the portal exposes only the approved tools and prompts from its upstream servers.
GA also brought the pieces that make that front door more usable in an organization: Gateway routing for HTTP logs and DLP scanning, policies for Code Mode, static OAuth credentials, session controls, service-token authentication, and Logpush support. Code Mode reduces the number of tool definitions placed in the model's context. Service tokens let a non-human agent authenticate without a browser.
The release matters because an operator can now put a common access and audit boundary in front of tools used by coding agents, incident-response agents, and operations assistants. It does not mean every named capability in the announcement is included on every plan. Logpush and broader DLP are the two important examples.
Cloudflare MCP Portals Pricing: The Active-User Boundary
The bill follows active identities, not the number of portals, servers, or tool calls. Cloudflare defines an active user as an identity that consumes a seat after an Access or Gateway authentication event. One identity consumes one seat regardless of how many applications it reaches or how often it logs in, according to the seat-management documentation.
That distinction changes the estimate:
- Ten engineers making thousands of calls still represent ten active user seats.
- One engineer using five MCP servers still represents one active user seat.
- A departed employee can continue occupying a seat until an administrator removes the user. Revoking sessions alone does not release it.
- An inactive record stops counting only after the user is removed from a seat. Cloudflare also offers configurable seat expiration.
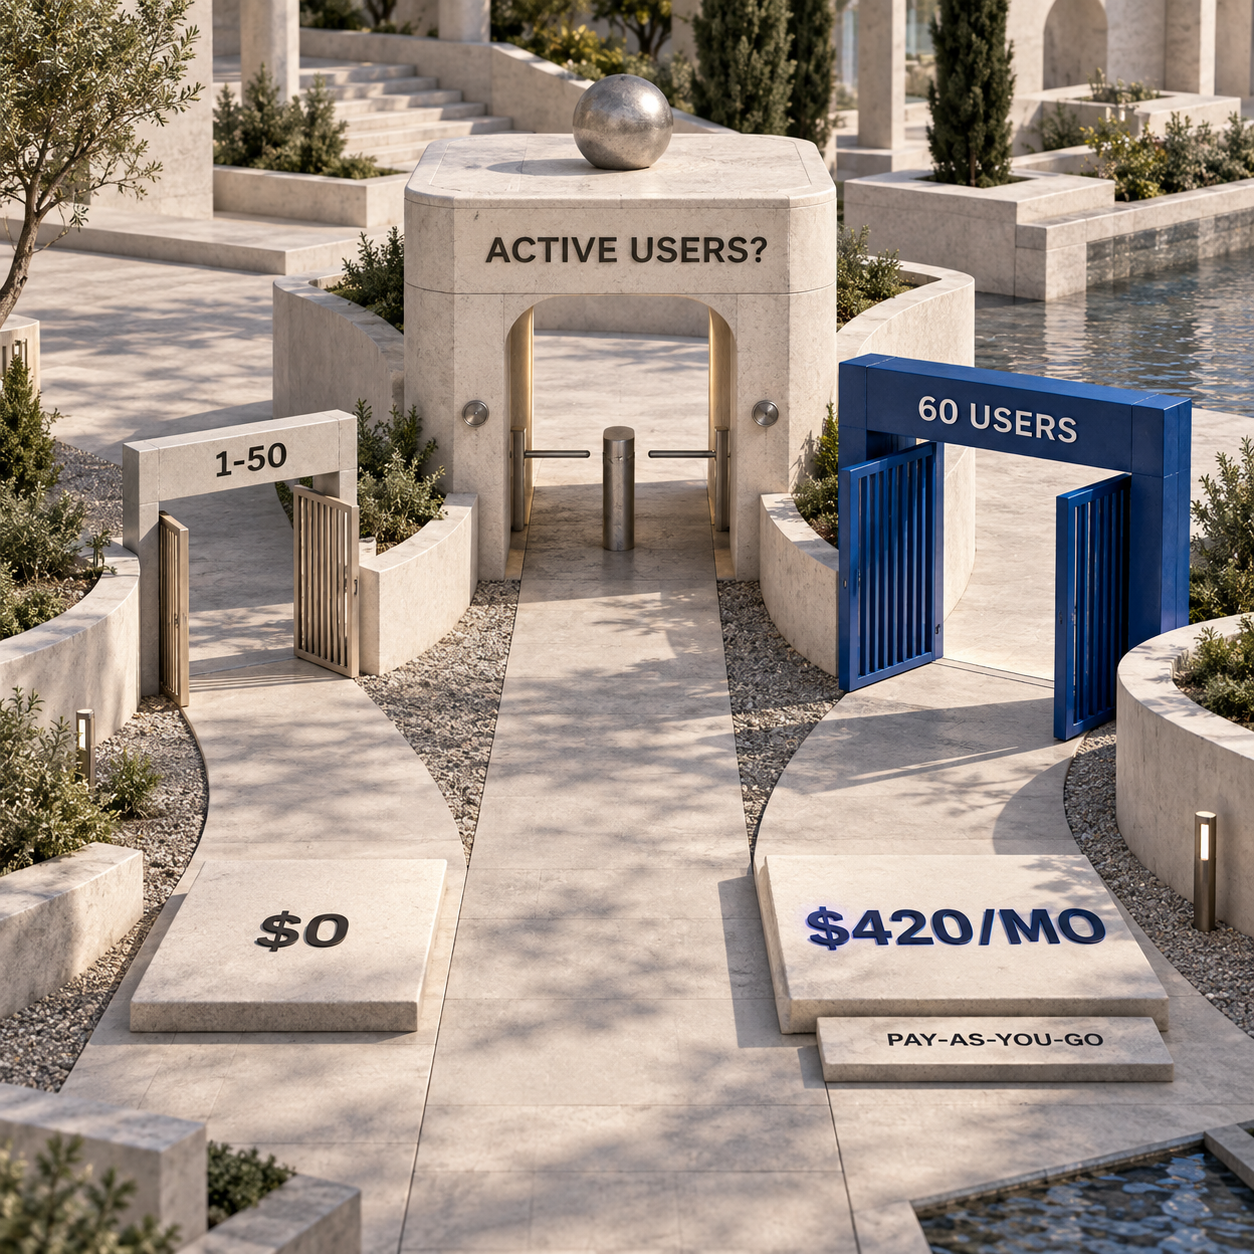
For a 60-active-user deployment on Pay-as-you-go, the calculation is 60 × $7 = $420 per month, or $5,040 per year, before every other service. The Free plan's 50-user limit is a separate plan boundary, not a permanent 50-seat credit to subtract from a Pay-as-you-go subscription.
Cloudflare MCP Portal Free Plan: What You Get
Free gives a small team the portal control plane within its 50-user Cloudflare One allowance. Cloudflare's default account limits document up to 20 MCP portals and 80 MCP servers per portal. The 80-server number is a technical capacity limit, not an allowance for 80 free users and not proof that every upstream service is free.
The useful Free-plan package is narrower and clearer:
- One governed endpoint for approved remote HTTP MCP servers.
- Access policies based on identity selectors such as email, group, country, and device posture.
- Tool, prompt, and resource activity in Cloudflare Access logs.
- Up to 24 hours of standard log retention under the current plan table.
- Selected predefined DLP profiles rather than the full Enterprise DLP surface.
For a five-person startup that needs a shared read-only issue tracker and observability endpoint, that can be enough. For a regulated operator that must export every agent action to a SIEM and retain it under a formal policy, it is not.
Cloudflare MCP Server Costs Sit Outside the Portal
The portal governs a request; it does not purchase the systems on either side of that request. Cloudflare's documented request path starts with an MCP client, passes through Access and the portal, then reaches an upstream MCP server that performs the work.
That creates four possible bills:
- Client model: Claude, ChatGPT, an API model, or another agent client may require its own seat or usage plan.
- Cloudflare One: the portal inherits the Free, Pay-as-you-go, or Contract user boundary described above.
- Upstream SaaS: a GitHub, Slack, incident-management, CRM, or database account may need its own subscription and user authorization.
- Server hosting: a self-hosted MCP server still consumes compute, storage, egress, and operator time wherever it runs.
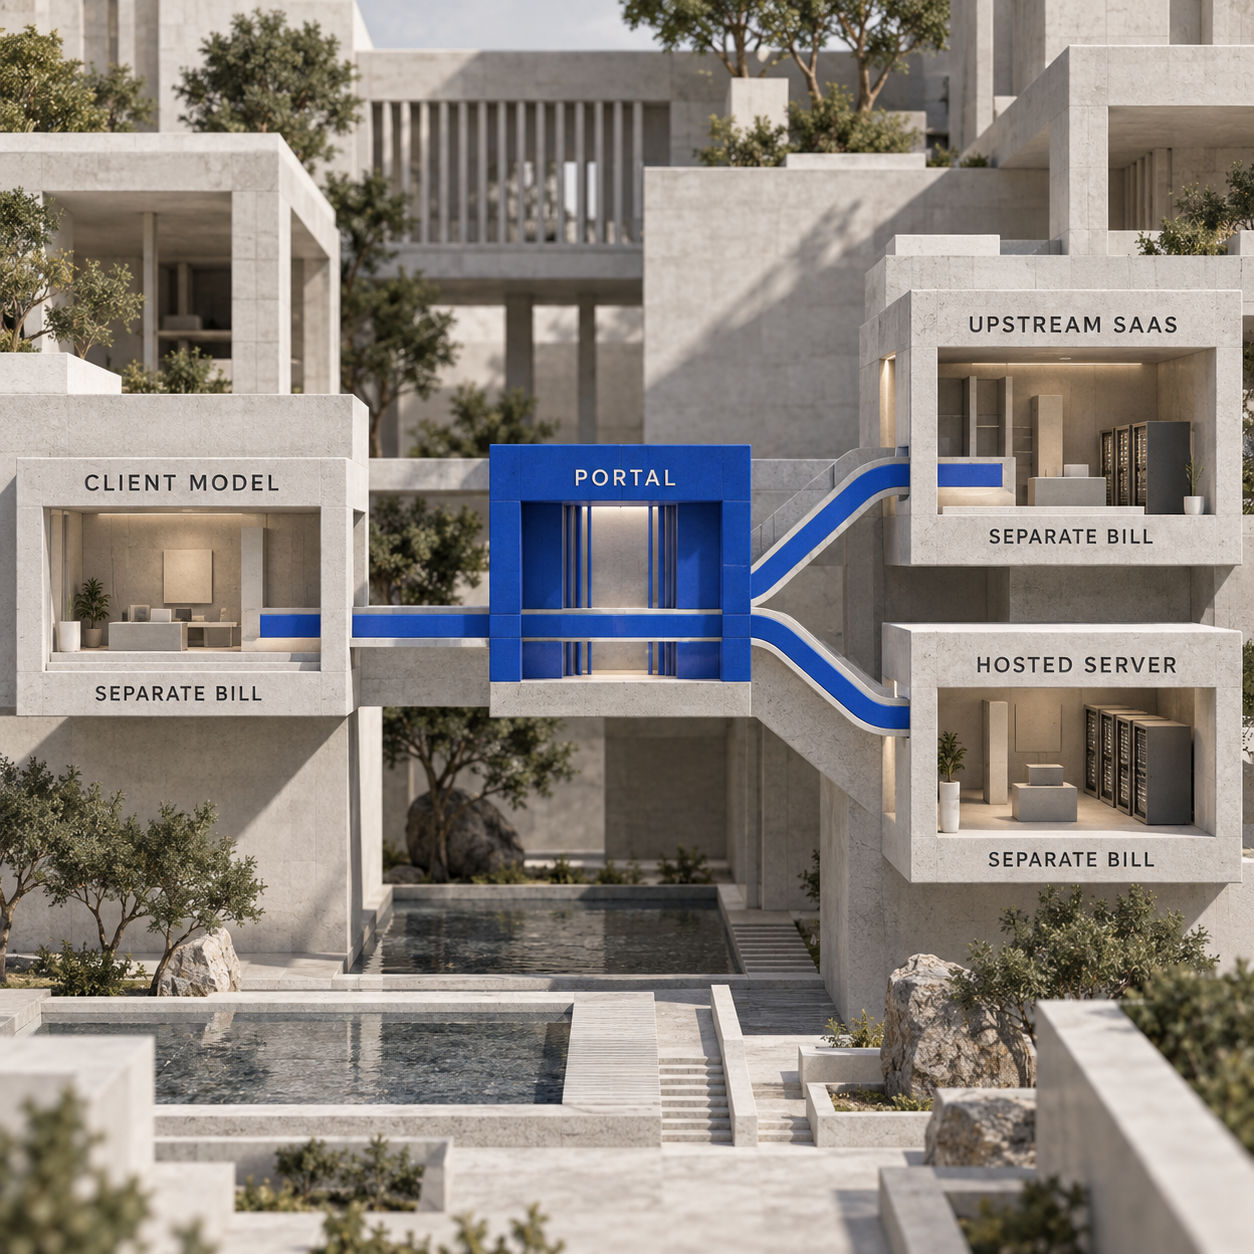
This separation is the most important protection against a misleading $0 estimate. A free portal can front a paid model and a paid SaaS account. It can also front a server on a free compute allowance today that becomes chargeable with traffic tomorrow.
The broader managed agent gateway comparison applies the same boundary across providers. If the decision is about Cloudflare as an edge and developer platform rather than this portal feature, the Cloudflare review covers that wider bill.
Security and Logging: Free Is Useful, Not Enterprise-Complete
Free includes meaningful controls, but GA capability and Free entitlement are not the same thing. Cloudflare's DLP documentation says broad Data Loss Prevention is an add-on to Zero Trust Enterprise. Free and Pay-as-you-go users can use the Financial Information and Social Security, Insurance, Tax, and Identifier Numbers predefined profiles, payload logging, and false-positive reporting.
Portal DLP also requires traffic to route through Cloudflare Gateway. Inspecting encrypted HTTP bodies requires Gateway HTTP filtering and TLS decryption. A team that merely creates a portal has not automatically turned on content inspection.
Logging has a similar boundary. The current plan table gives Free up to 24 hours of standard retention and Pay-as-you-go up to 30 days. Cloudflare's Zero Trust Logpush integration is Enterprise-only, and MCP Portal Logs is one of its supported export datasets.
There are policy limits too. When a server is authorized through a portal, Cloudflare says independent MFA, purpose justification, and temporary authentication are not enforced for that server authorization. Email, group, country, and device-posture selectors still apply. A security buyer should review that distinction before treating the portal as a universal approval gate.
If those controls are the center of the purchase, compare the dedicated MCP identity and access options instead of assuming the longest Cloudflare feature list is the best fit.
What It Means for Builders, Operators, and Buyers
Builders: the first wall is transport
Builders can place remote HTTP MCP servers behind the portal, including servers protected by OAuth, bearer tokens, or custom headers. A local stdio-only server cannot be added directly. Cloudflare says it must first be hosted behind an HTTP endpoint.
Compatibility is not automatic after that conversion. Some upstream providers reject proxy-based clients and return a 403 during registration. Manual OAuth configurations can wait for the first user's authorization, and admin OAuth tokens can expire without a notification. The server then moves to Error or Sync Required and disappears from users until an administrator reauthenticates it.
The 80-server-per-portal cap is unlikely to constrain a small pilot. The harder wall is ownership: someone must watch server state, rotate credentials, review new tools, and decide whether a tool stays read-only.
Operators: seat hygiene is part of cost control
Operators should monitor Zero Trust > Team & Resources > Users, not infer billing from employee headcount or tool-call volume. Remove departed identities, turn on seat expiration when it matches policy, and keep human access separate from machine credentials.
Start with one low-risk portal and one remote server that exposes a reversible read action. A read-only issue lookup or documentation search produces useful logs without giving a new control plane permission to deploy code, delete records, or change customer data.
Buyers: audit requirements decide the tier before headcount does
A 30-person organization can fit Free by headcount and still require Contract because its evidence policy needs Logpush or a broader DLP surface. A 60-person organization with light security requirements lands on Pay-as-you-go because it exceeds Free's user limit even if it makes only a few tool calls.
The purchase rule is therefore two-dimensional: count active identities, then map the required security evidence. Headcount sets the minimum plan. Audit and DLP requirements can move the organization higher.
Who Should Act Now, Who Should Wait, and Who Is Unaffected
Act now if 2 to 50 active people already use several remote HTTP MCP servers and the immediate problem is shared access, narrower tool exposure, and recent activity logs. Free is a sensible pilot when the upstream permissions are read-only and a 24-hour review window is enough.
Wait or negotiate if the first deployment must export portal events to a SIEM, retain logs for months, scan with custom DLP profiles, or enforce an approval step that the portal's policy model does not support. Those are buying requirements, not settings to discover after rollout.
Stay unaffected if one developer connects directly to one trusted MCP server and has no team policy or audit need. A portal would add another authentication and failure surface without solving a current problem.
The Monday move
Run one narrow entitlement check before connecting production tools:
Record the plan and active seats
Open Cloudflare One and record the account plan plus the active-user count shown on the overview. Then open Team & Resources > Users and identify identities that still consume seats.
Add one read-only remote HTTP server
Choose a server whose tool cannot write, deploy, delete, or change billing. Confirm that it exposes a remote HTTP endpoint; a local stdio server is not a valid test target.
Create the smallest portal policy
Allow one test identity, expose only the single read-only tool, and keep the upstream scope minimal. Record whether the server requires per-user OAuth or can use a service token.
Make one call and compare the screens
Authenticate once, invoke the read-only tool, then compare the active-user count, recent portal logs, and billing screen with the values recorded before the call. The expected cost event is the identity authentication, not the tool invocation. Treat the dashboard result for your account as the final entitlement check.
What's Overhyped About the Free Portal
The word free can easily absorb costs that belong to three other systems. Cloudflare does not pay the client model, the upstream subscription, or a server you host. It also does not turn a local-only stdio tool into a remote service without hosting work.
The security story needs the same restraint. GA added Gateway routing, DLP integration, Code Mode policy, service tokens, session management, and Logpush support. Free does not therefore include every DLP profile or Logpush export. A feature can exist in the product while its useful enterprise form requires a higher plan.
Finally, a portal is not an authorization cure-all. It centralizes policy and visibility, but upstream OAuth still matters, tokens still expire, proxy compatibility still varies, and some high-assurance policy features do not apply during server authorization through a portal.
The durable claim is smaller: Cloudflare now offers a practical $0 front door for a team of up to 50 active users, provided the team understands what remains outside that door.
Frequently Asked Questions
Is Cloudflare free or paid?
Both. Cloudflare sells many products, but the relevant Cloudflare One plans are Free at $0 for up to 50 users, Pay-as-you-go at $7 per user per month, and a custom annual Contract plan.
Does Cloudflare have an MCP server?
Yes. Cloudflare runs a catalog of managed remote MCP servers, while MCP server portals are the access and governance layer that can combine approved servers behind one endpoint.
How to host a MCP server for free?
A Cloudflare portal can be free within the 50-user limit, but portal access is not server hosting. You still need a remote HTTP MCP endpoint on your own infrastructure or a provider's service, and that hosting layer has its own allowance and bill.
Does the US government use Cloudflare?
Cloudflare offers a public-sector platform that it describes as FedRAMP High and GovRAMP Moderate Authorized. That confirms a government-ready offering, not which specific agencies are customers, and it does not change MCP portal pricing.
Why is Cloudflare falling?
The question is ambiguous. A stock-price move needs current market reporting; a failing portal request needs the server status, Access policy, OAuth state, and Gateway path checked. Neither changes the published Free and Pay-as-you-go plan boundaries.
Who is Cloudflare's biggest competitor?
There is no single answer across CDN, Zero Trust, developer compute, and MCP governance. The relevant competitor depends on the layer you are buying; for this decision, compare governed MCP access rather than an entire connectivity cloud.
What can replace Cloudflare?
Replacement is layer-specific. A CDN can replace delivery, an identity-aware proxy can replace Access, and an MCP gateway can replace portal governance, but one product may not replace all three together.
Is Cloudflare a Russian company?
No. Cloudflare lists its headquarters at 101 Townsend Street in San Francisco.
Who are the biggest clients of Cloudflare?
Cloudflare publishes named customer case studies, but it does not publish a revenue-ranked list that supports a definitive "biggest clients" answer.
Want the next agent-infrastructure change translated into a budget and rollout decision? Join the newsletter.
- Last Updated
- Sep 26, 2026
- Category
- Build
Prefer this site in Google


Mark omidsaffari.com as preferred and Google lifts it in Top Stories, AI Overviews and AI Mode for you.

How to Use Agentic CUDA Optimizer
Set up the CUDA optimizer, run a bounded kernel experiment, and check correctness, GPU time and model costs before trusting a speedup.Sep 25, 2026Build
Runpod Pricing (2026): Pods or Serverless by Paid Time
Calculate Runpod pricing for Pods, Serverless, storage and production inference, with a dated H100 worksheet and a billable-time break-even.Sep 25, 2026Build
How to Use Vercel Sandbox Drives
Keep an agent workspace across Vercel Sandbox runs. Create a Drive, mount it, restart safely, and understand writer, snapshot, and region limits.Sep 25, 2026Build
Firecrawl Alternatives
Compare Firecrawl alternatives for business AI pipelines by crawl support, Markdown and JSON output, migration work and cost per usable page.Sep 25, 2026Build
CodeRabbit Alternatives
Compare CodeRabbit alternatives by Git support, hosting, review limits and real team cost, with clear reasons to switch or stay.Sep 25, 2026Build
Greptile vs CodeRabbit
Compare Greptile and CodeRabbit on review limits, real team costs, Git support and the checks to run before buying.Sep 25, 2026Build
How to Use Perplexity Portable Computer
Set up Perplexity Portable Computer on a supported Windows PC, choose a local model, and test a recurring file task with clear cloud permissions.Sep 25, 2026Build